

ActualTestsQuiz SC-400 Exam Questions | Real SC-400 Practice Dumps
Verified SC-400 Exam Dumps Q&As - Provide SC-400 with Correct Answers
NEW QUESTION # 123
You need to recommend a solution that meets the compliance requirements for viewing DLP tooltip justifications.
What should you recommend?
- A. Instruct the compliance department users to review the DLP incidents report.
- B. Instruct the compliance department users to review the False positive and override report.
- C. Configure a Microsoft Power Automate workflow to route DLP notification emails to the compliance department.
- D. Configure an Azure logic app to route DLP notification emails to the compliance department.
Answer: B
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/view-the-dlp-reports?view=o365-worldwide
NEW QUESTION # 124
You have a Microsoft 365 tenant that uses data loss prevention (DLP) to protect sensitive information.
You create a new custom sensitive info type that has the matching element shown in the following exhibit.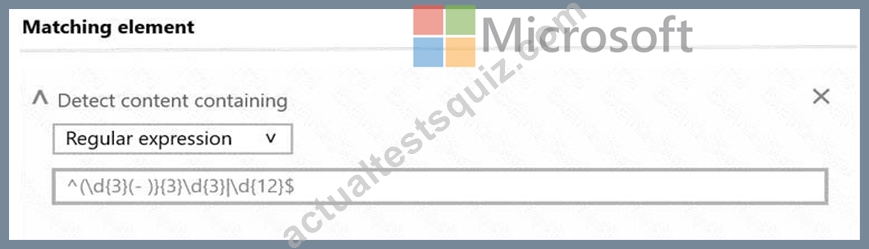
The supporting elements are configured as shown in the following exhibit.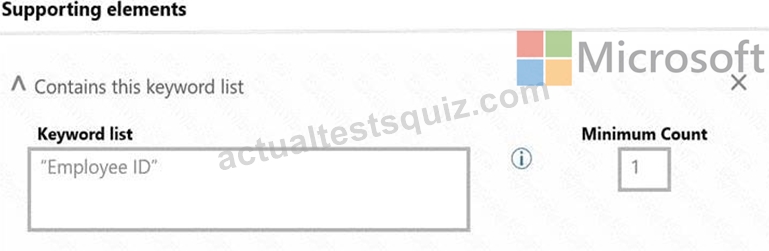
The confidence level and character proximity are configured as shown in the following exhibit.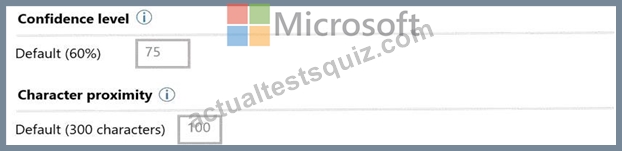
For each of the following statements, select Yes if statement is true. Otherwise, select No NOTE: Each correct selection is worth one point.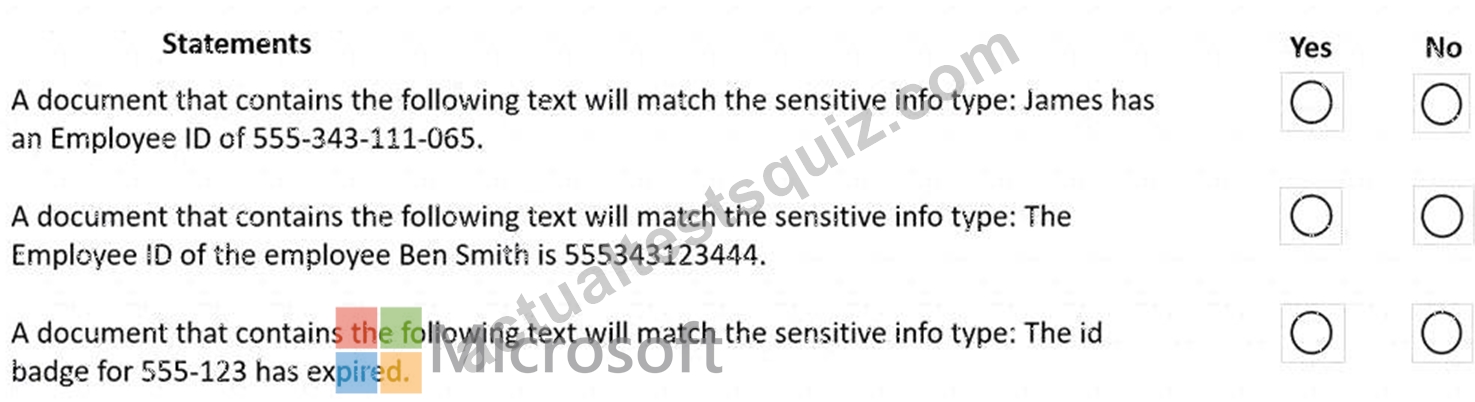
Answer:
Explanation: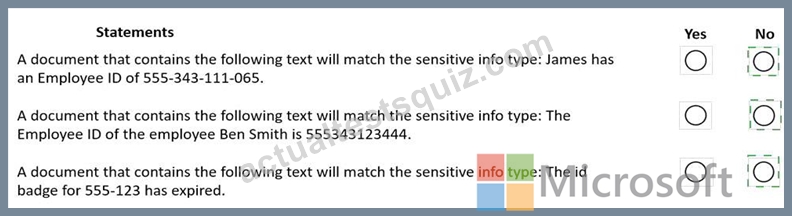
Explanation
Graphical user interface, text, application, email Description automatically generated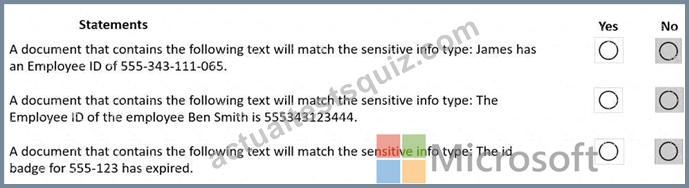
Note: The regular expression has a starts with (^) and ends with ($) metacharacter and will not match any of the sentences. Without the starts with (^) metacharacter the first and second sentences would match and the supporting element (Employee ID) would be within 100 character proximity.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/create-a-custom-sensitive-information-type?view=o
NEW QUESTION # 125
You plan to implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You need to identify which end user activities can be audited on the endpoints, and which activities can be restricted on the endpoints.
What should you identify for each activity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.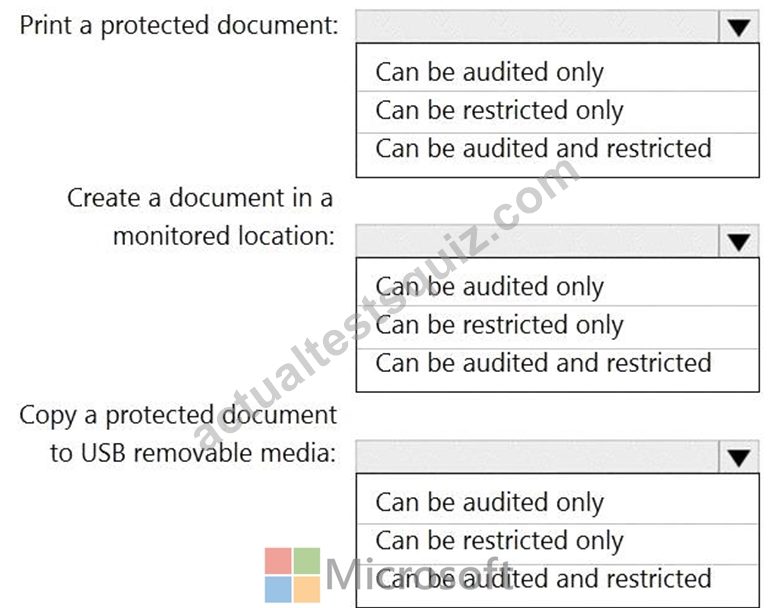
Answer:
Explanation: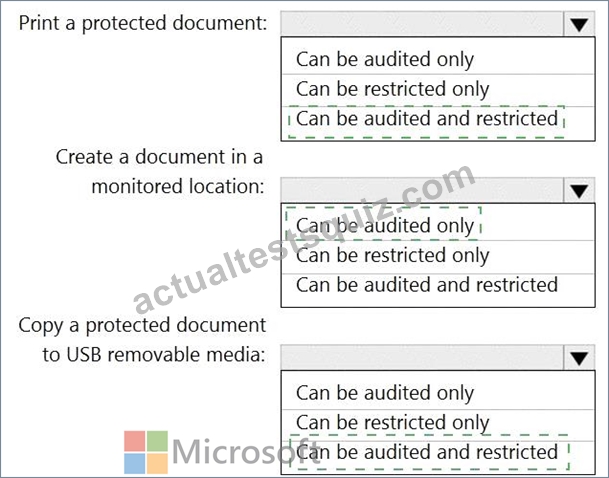
Explanation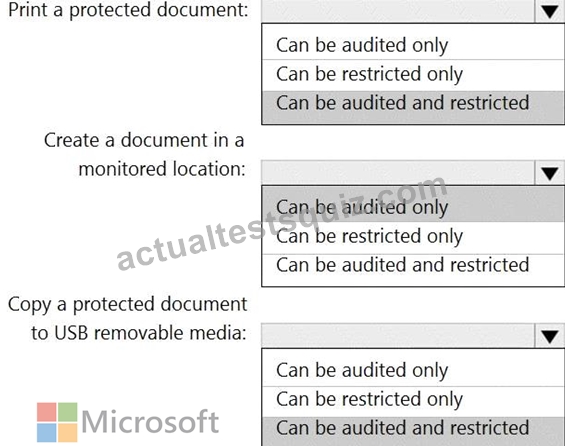
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-learn-about?view=o365-worldwide
NEW QUESTION # 126
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You have computers that run Windows 10 and have Microsoft 365 Apps installed. The computers are joined to Azure Active Directory (Azure AD).
You need to ensure that Endpoint DLP policies can protect content on the computers.
Solution: You deploy the unified labeling client to the computers.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
Explanation
Explanation/Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-getting-started?view=o365-worldwide
NEW QUESTION # 127
You create a sensitivity label as shown in the Sensitivity Label exhibit.
You create an auto-labeling policy as shown in the Auto Labeling Policy exhibit.
A user sends the following email:
From: [email protected]
To: [email protected]
Subject: Address List
Message Body:
Here are the lists that you requested.
Attachments:
<<File1.docx>>
<<File2.xml>>
Both attachments contain lists of IP addresses.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.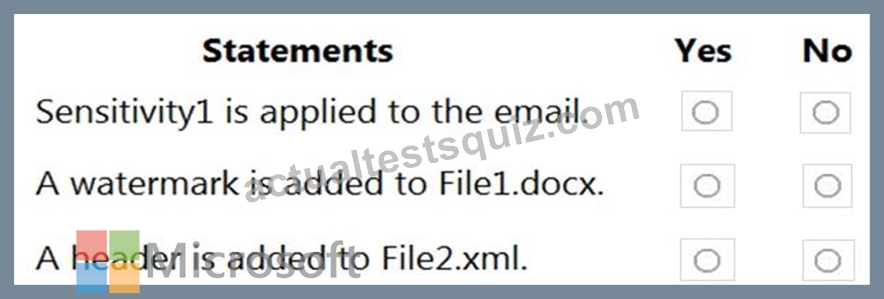
Answer:
Explanation: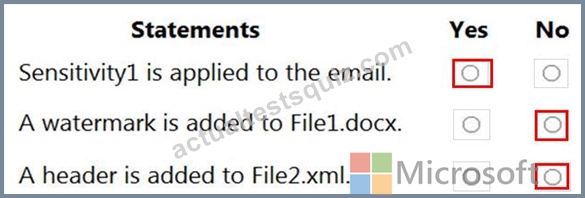
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365-worldwide
NEW QUESTION # 128
You have a Microsoft 365 tenant that uses trainable classifiers.
You are creating a custom trainable classifier.
You collect 300 sample file types to use as seed content Some of the file samples are encrypted.
You organize the files into categories as shown in the following table.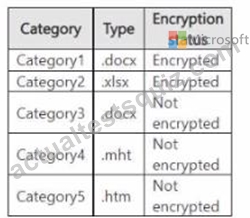
Which file categories can be used as seed content?
- A. Category1 and Category3 only
- B. Category3 only
- C. Category1, Category2, Category3. Category4 and Category5
- D. Category3, Category4 and Category5 only
- E. Category3 and Category5 only
Answer: E
NEW QUESTION # 129
You have a Microsoft 365 subscription that contains two groups named Group1 and Group2.
You have the compliance assessments shown in the following table.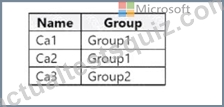
You have the improvement actions shown in the following table.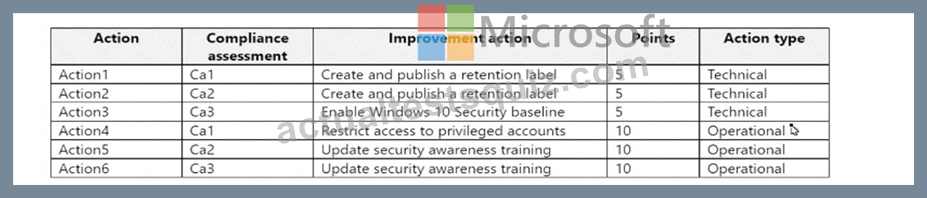
You perform the following actions:
* Create and publish a retention label.
* Implement security awareness training for all users.
* For Action4, change Implementation status to Implemented
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.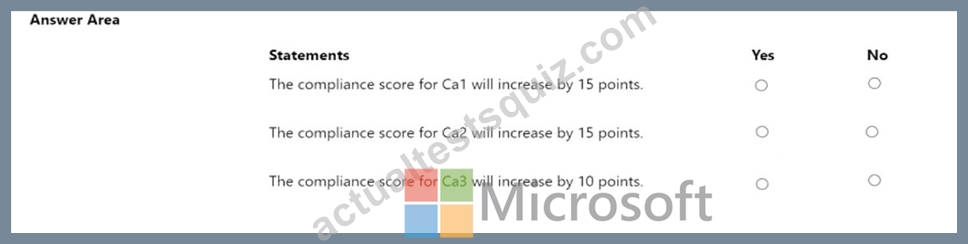
Answer:
Explanation: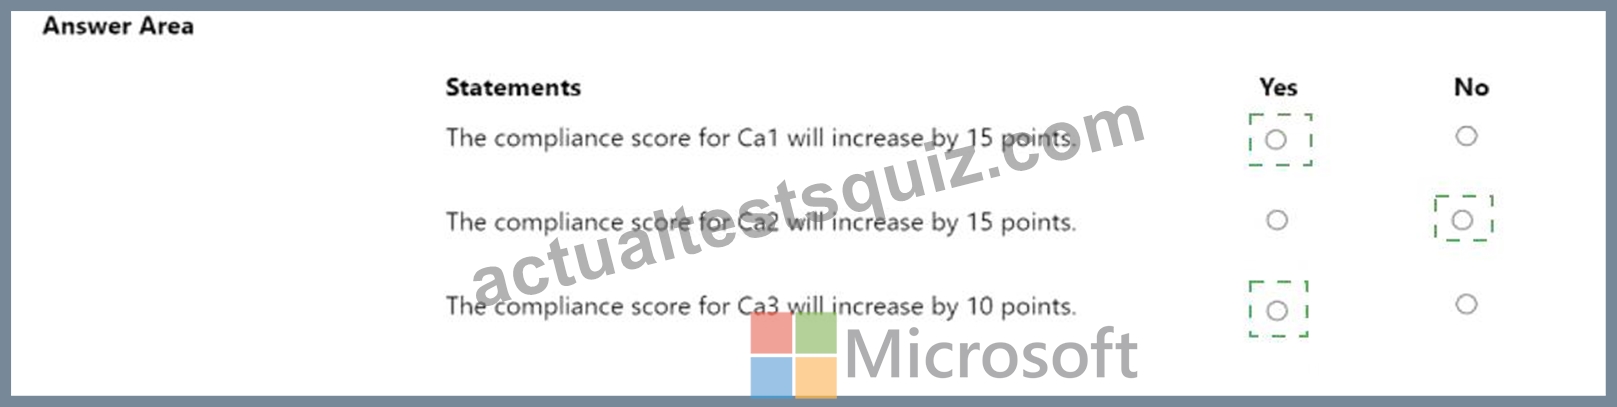
Explanation: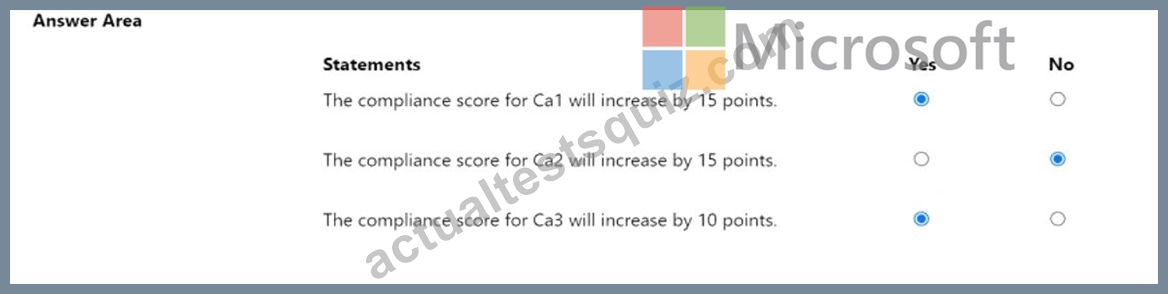
NEW QUESTION # 130
You have a Microsoft SharePoint Online site named Site1 that contains the files shown in the following table.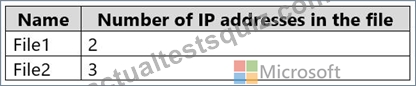
You have a data loss prevention (DLP) policy named DLP1 that has the advanced DLP rules shown in the following table.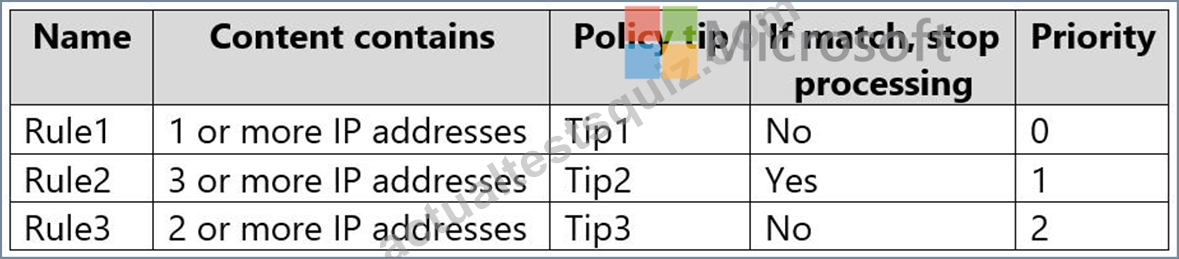
You apply DLP1 to Site1.
Which policy tips will appear for File2?
- A. Tip1 and Tip2 only
- B. Tip3 only
- C. Tip1 only
- D. Tip2 only
Answer: D
NEW QUESTION # 131
You have the retention label shown in the Retention exhibit. (Click the Retention tab.) Users apply the retention label to files and set the asset ID as shown in the following table.
On December 1, 2020. you create the event shown in the Event exhibit. (Click the Event tab.) For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: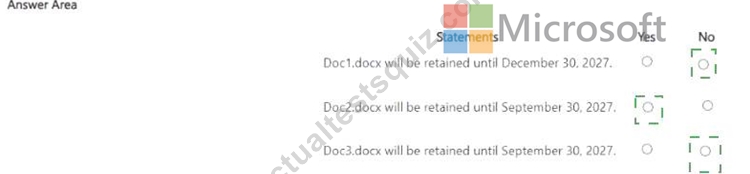
NEW QUESTION # 132
You have a data loss prevention (DLP) policy configured for endpoints as shown in the following exhibit.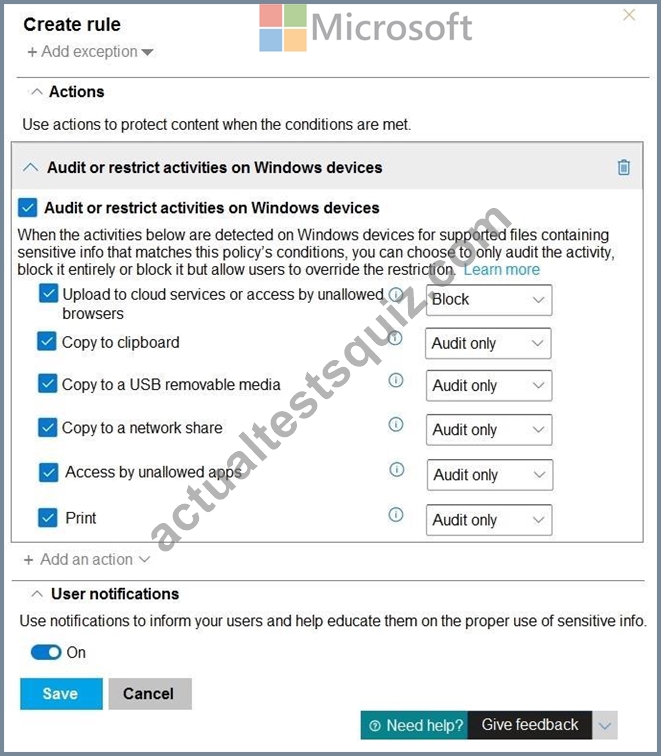
From a computer named Computer1, a user can sometimes upload files to cloud services and sometimes cannot. Other users experience the same issue.
What are two possible causes of the issue? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
- A. The computers are NOT onboarded to the Microsoft 365 compliance center.
- B. The Copy to clipboard action is set to Audit only.
- C. There are file path exclusions in the Microsoft 365 Endpoint data loss prevention (Endpoint DIP) settings.
- D. The Access by unallowed apps action is set to Audit only.
- E. The unallowed browsers in the Microsoft 365 Endpoint data loss prevention (Endpoint DLP) settings are NOT configured.
Answer: C,E
Explanation:
Detects when a user attempts to upload an item to a restricted service domain or access an item through a browser. If they are using a browser that is listed in DLP as an unallowed browser, the upload activity will be blocked and the user is redirected to use Microsoft Edge . Microsoft Edge will then either allow or block the upload or access based on the DLP policy configuration So if unallowed browser is NOT configured you can use chrome/etc with impugnity anc won't be kicked over to edge which observes the DLP policy, in other words, sometimes can upload (chrome), sometimes can not (edge).
NEW QUESTION # 133
You have a Microsoft 365 E5 subscription that contains the groups shown in the following table.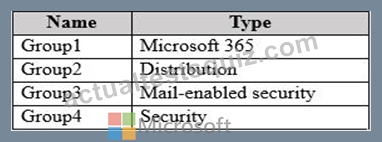
You need to create a Privacy Risk Management policy in Microsoft Priva.
To which groups can you apply the policy?
- A. Group1 only
- B. Group1, Group2, Group3, and Group4
- C. Group1, Group2, and Group3 only
- D. Group1 and Group2 only
- E. Group1, Group3, and Group4 only
Answer: A
Explanation:
https://learn.microsoft.com/en-us/privacy/priva/risk-management-policies#choose-users-and- groups
NEW QUESTION # 134
You have a Microsoft 365 E5 subscription.
You need to create static retention policies for the following locations:
- Teams chats
- Exchange email
- SharePoint sites
- Microsoft 365 Groups
- Teams channel messages
What is the minimum number of retention policies required?
- A. 0
- B. 1
- C. 2
- D. 3
- E. 4
Answer: B
Explanation:
If you select the Teams or Yammer locations when you create a retention policy, the other locations are automatically excluded. This means that the instructions to follow depend on whether you need to include the Teams or Yammer locations.
https://learn.microsoft.com/en-us/microsoft-365/compliance/create-retention-policies?view=o365- worldwide&tabs=teams-retention#create-and-configure-a-retention-policy
NEW QUESTION # 135
You have a Microsoft 365 E5 subscription that contains the groups shown in the following table.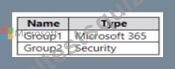
The subscription contains the resources shown in the following table.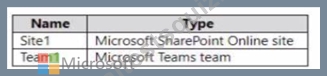
You create a sensitivity label named Label 1.
You need to publish Label! and have the label apply automatically.
To what can you publish Label 1, and to what can Label! be auto-applied? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.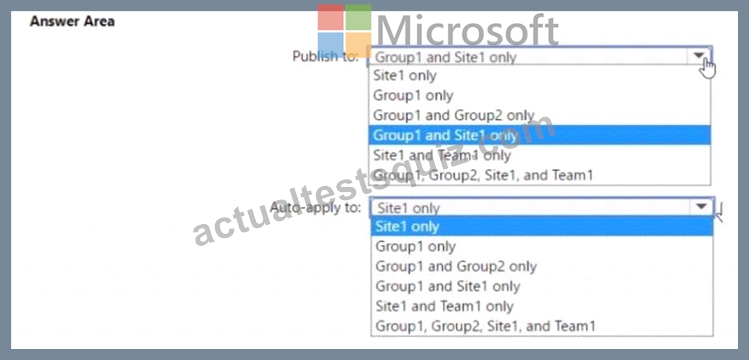
Answer:
Explanation: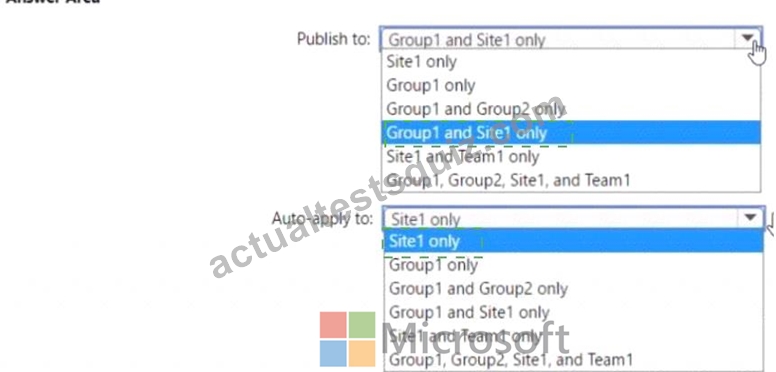
Explanation: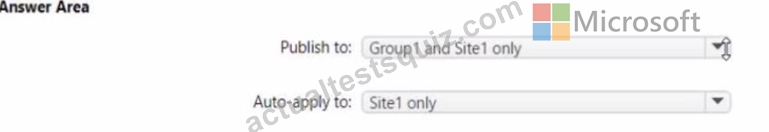
NEW QUESTION # 136
Case Study 1 - Fabrikam, Inc
Overview
Fabrikam, Inc. is a consulting company that has a main office in Montreal and six branch offices in New York, Seattle, Miami, Houston, Los Angeles, and Vancouver.
Existing Environment
Cloud Environment
Fabrikam has a Microsoft 365 tenant that contains the following resources:
An Azure Active Directory (Azure AD) tenant that syncs to an on-premises Active Directory domain named corp.fabrikam.com Microsoft Cloud App Security connectors configured for all supported cloud applications used by the company Some users have company Dropbox accounts.
Compliance Configuration
Fabrikam has the following in the Microsoft 365 compliance center:
A data loss prevention (DLP) policy is configured. The policy displays a tooltip to users. Users can provide a business justification to override a DLP policy violation.
The Azure Information Protection unified labeling scanner is installed and configured.
A sensitivity label named Fabrikam Confidential is configured.
An existing third-party records management system is managed by the compliance department.
Human Resources (HR) Management System
The HR department has an Azure SQL database that contains employee information. Each employee has a unique 12-character alphanumeric ID. The database contains confidential employee attributes including payroll information, date of birth, and personal contact details.
On-Premises Environment
You have an on-premises file server that runs Windows Server 2019 and stores Microsoft Office documents in a shared folder named Data.
All end-user computers are joined to the corp.fabrikam.com domain and run a third-party antimalware application.
Business Processes
Sales Contracts
Users in the sales department receive draft sales contracts from customers by email. The sales contracts are written by the customers and are not in a standard format.
Employment Applications
Employment applications and resumes are received by HR department managers and stored in either mailboxes, Microsoft SharePoint Online sites, OneDrive for Business folders, or Microsoft Teams channels.
The employment application form is downloaded from SharePoint Online and a serial number is assigned to each application.
The resumes are written by the applicants and are in any format.
Requirements
HR Requirements
You need to create a DLP policy that will notify the HR department of a DLP policy violation if a document that contains confidential employee attributes is shared externally. The DLP policy must use an Exact Data Match (EDM) classification derived from a CSV export of the HR department database.
The HR department identifies the following requirements for handling employment applications:
Resumes must be identified automatically based on similarities to other resumes received in the past.
Employment applications and resumes must be deleted automatically two years after the applications are received.
Documents and emails that contain an application serial number must be identified automatically and marked as an employment application.
Sales Requirements
A sensitivity label named Sales Contract must be applied automatically to all draft and finalized sales contracts.
Compliance Requirements
Fabrikam identifies the following compliance requirements:
All DLP policies must be applied to computers that run Windows 10, with the least possible changes to the computers.
Users in the compliance department must view the justification provided when a user receives a tooltip notification for a DLP violation.
If a document that has the Fabrikam Confidential sensitivity label applied is uploaded to Dropbox, the file must be deleted automatically.
The Fabrikam Confidential sensitivity label must be applied to existing Microsoft Word documents in the Data shared folder that have a document footer containing the following string: Company use only.
Users must be able to manually select that email messages are sent encrypted. The encryption will use Office 365 Message Encryption (OME) v2. Any email containing an attachment that has the Fabrikam Confidential sensitivity label applied must be encrypted automatically by using OME.
Existing policies configured in the third-party records management system must be replaced by using Records management in the Microsoft 365 compliance center. The compliance department plans to export the existing policies, and then produce a CSV file that contains matching labels and policies that are compatible with records management in Microsoft 365.
The CSV file must be used to configure records management in Microsoft 365.
Executive Requirements
You must be able to restore all email received by Fabrikam executives for up to three years after an email is received, even if the email was deleted permanently.
You need to recommend a solution that meets the compliance requirements for protecting the documents in the Data shared folder.
What should you recommend?
- A. From Azure Information Protection, configure a content scan job.
- B. From the Microsoft 365 compliance center, configure a DLP policy.
- C. From the Microsoft 365 compliance center, configure an auto-labeling policy.
- D. From the Microsoft 365 compliance center, configure a Content Search query.
Answer: A
Explanation:
You run an AIP scanner on premise. You cannot configure auto labeling from compliance center on premise.
NEW QUESTION # 137
You need to provide a user with the ability to view data loss prevention (DLP) alerts in the Microsoft 365 compliance center. The solution must use the principle of least privilege.
Which role should you assign to the user?
- A. Compliance data administrator
- B. Security operator
- C. Compliance administrator
- D. Security reader
Answer: D
Explanation:
If you want to view the DLP alert management dashboard or to edit the alert configuration options in a DLP policy, you must be a member of one of these role groups:
Compliance Administrator
Compliance Data Administrator
Security Administrator
Security Operator
Security Reader
To access the DLP alert management dashboard, you need the Manage alerts role and either of the following roles:
DLP Compliance Management
View-Only DLP Compliance Management
https://docs.microsoft.com/en-us/microsoft-365/compliance/dlp-configure-view-alerts- policies?view=o365-worldwide#roles
NEW QUESTION # 138
You need to protect documents that contain credit card numbers from being opened by users outside your company. The solution must ensure that users at your company can open the documents.
What should you use?
- A. a retention policy
- B. a sensitivity label policy
- C. a data loss prevention (DLP) policy
- D. a sensitivity label
Answer: C
Explanation:
Reference:
https:/ HYPERLINK "https://docs.microsoft.com/en-us/microsoft-365/compliance/dlp-learn-about-dlp?
view=o365-worldwide"/docs.microsoft.com/en-us/microsoft-365/compliance/dlp-learn-about-dlp?vi HYPERLINK "https://docs.microsoft.com/en-us/microsoft-365/compliance/dlp-learn-about-dlp?view=o365- worldwide"ew=o365-worldwide
NEW QUESTION # 139
You have a Microsoft 365 E5 tenant that contains the policies shown in the following table.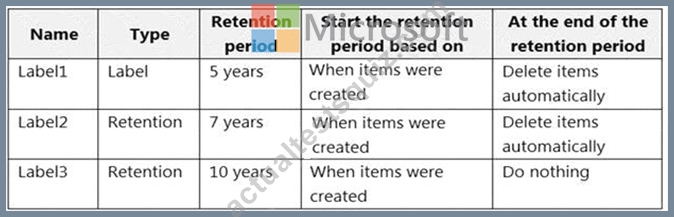
A file named File1 has all the policies applied.
How long will File1 be retained?
- A. File1 will be deleted automatically after seven years.
- B. File1 will be retained until the file is deleted manually.
- C. File1 will be deleted automatically after five years.
- D. File1 will be deleted automatically after 10 years.
Answer: D
NEW QUESTION # 140
You create a data loss prevention (DLP) policy. The Advanced DLP rules page is shown in the Rules exhibit.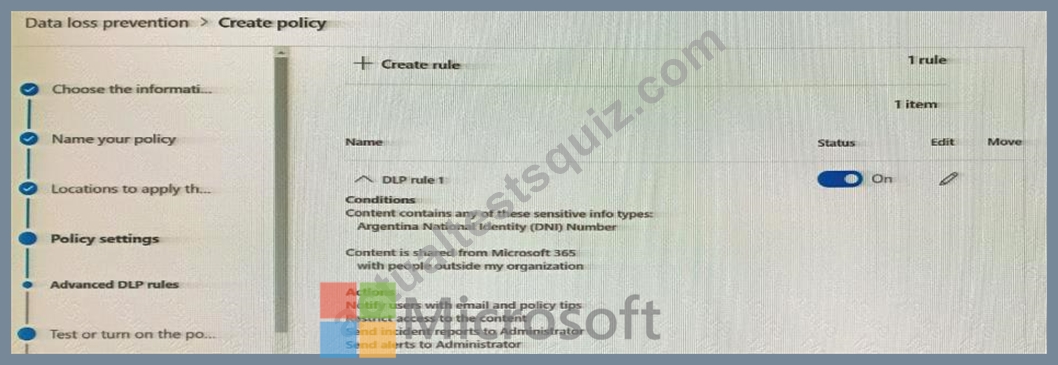
The Review your settings page is shown in the review exhibit.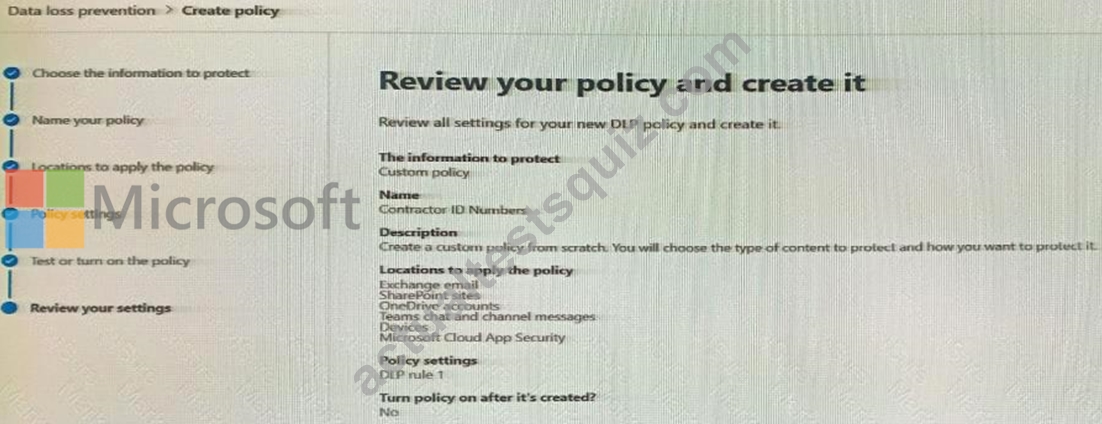
You need to review the potential impact of enabling the policy without applying the actions.
What should you do?
- A. Edit the policy, remove the Restrict access to the content and Send incident report to Administrator actions, and then select Yes, turn it on right away.
- B. Edit the policy, remove all the actions in DLP rule 1, and select I'd like to test it out first.
- C. Edit the policy, remove all the actions in DLP rule 1, and select Yes, turn it on right away.
- D. Edit the policy, and then select I'd like to test it out first.
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/create-a-dlp-policy-from-a-template?view=o365-wo
NEW QUESTION # 141
You have the retention label policy shown in the Policy exhibit. (Click the Policy tab.)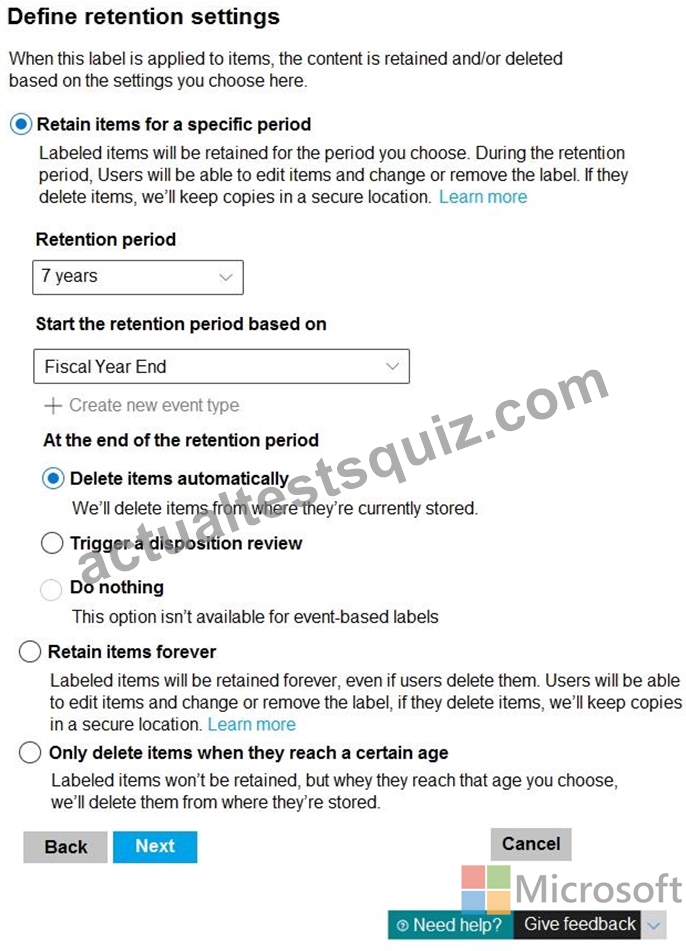
Users apply the retention label policy to files and set the asset ID as shown in the following table.
On December 1, 2020, you create the event shown in the Event exhibit. (Click the Event tab.)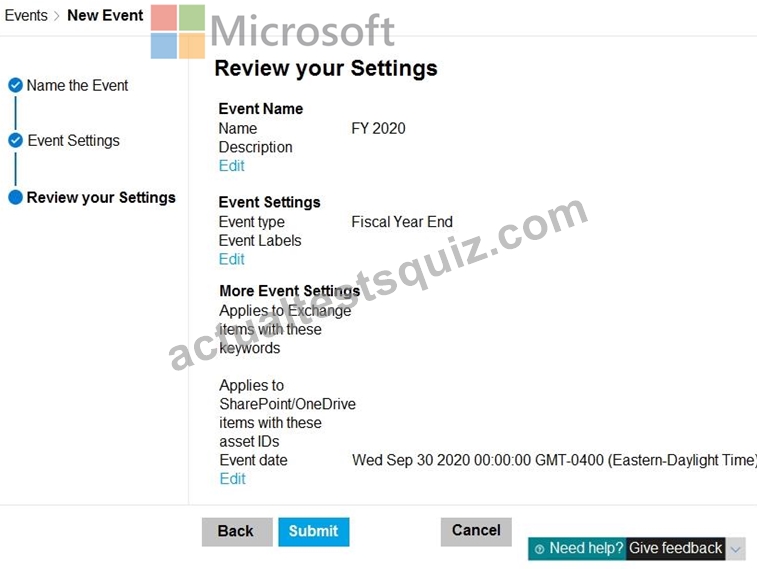
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.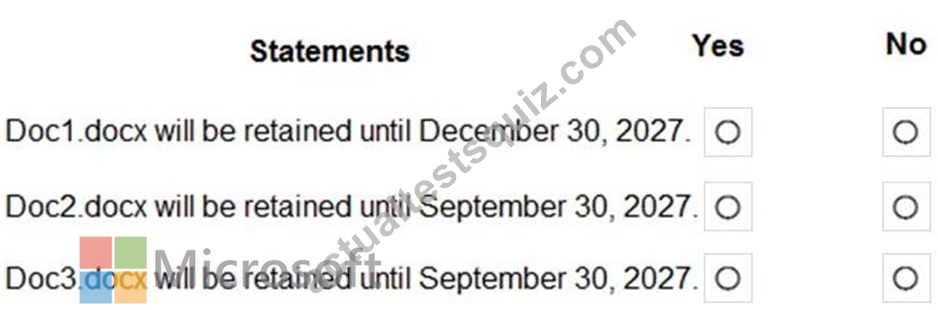
Answer:
Explanation: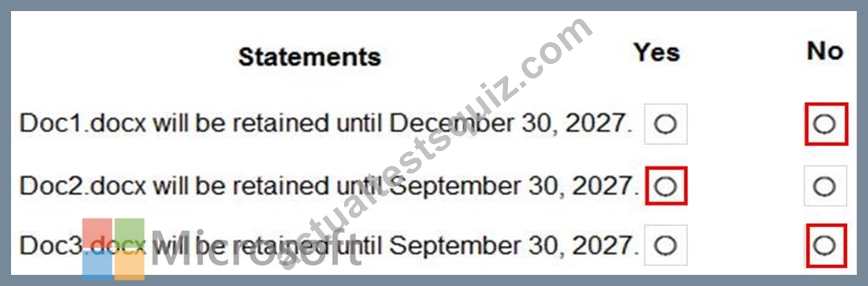
NEW QUESTION # 142
You plan to implement a sensitive information type based on a trainable classifier. The sensitive information type will identify employment contracts.
You need to copy the required files to Microsoft SharePoint Online folders to train the classifier.
What should you use to seed content and test the classifier? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.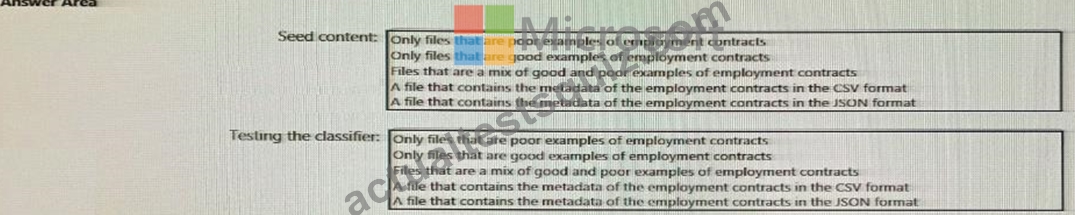
Answer:
Explanation: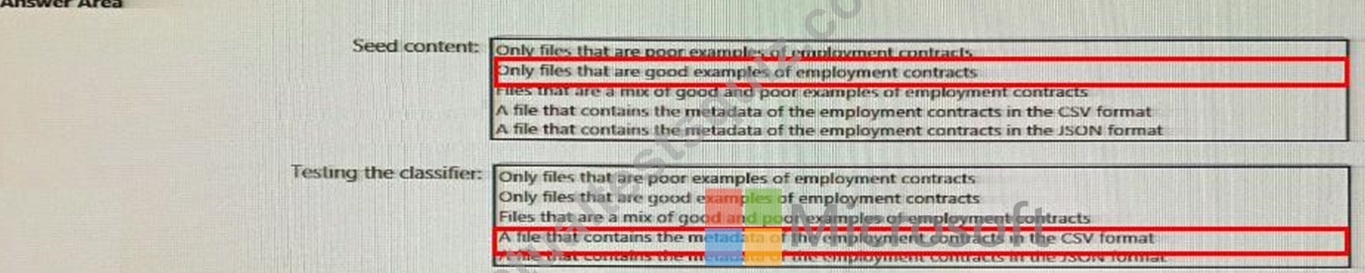
NEW QUESTION # 143
You need to recommend an information governance solution that meets the HR requirements for handling employment applications and resumes.
What is the minimum number of information governance solution components that you should create? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.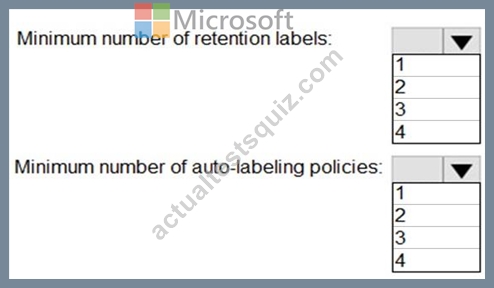
Answer:
Explanation: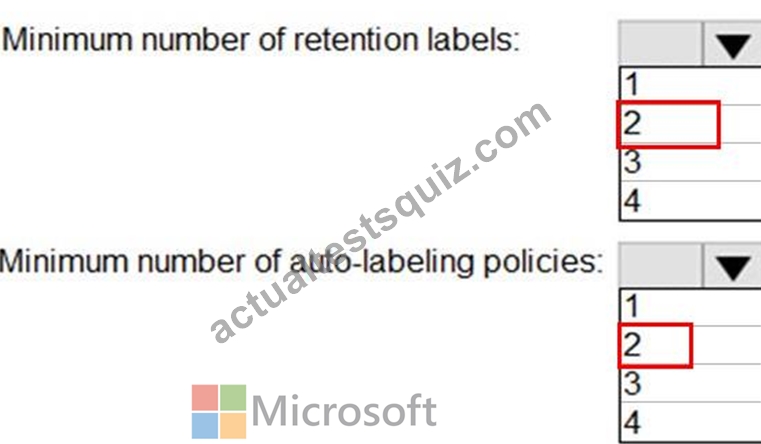
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-retention-labels-automatically?view=o365-worldwide
Topic 3, Mix Questions
Mix Questions
SC-400 Mix Questions IN THIS CASE STUDY
NEW QUESTION # 144
You have a Microsoft 365 tenant that uses trainable classifiers.
You are creating a custom trainable classifier.
You collect 300 sample file types from various geographical locations to use as seed content. Some of the file samples are encrypted.
You organize the files into categories as shown in the following table.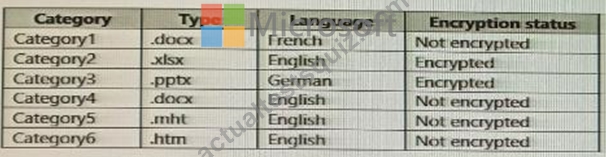
Which file categories can be used as seed content?
- A. Category1 and Category3 only
- B. Category2. Category3. and Category5 only
- C. Category4 and Category6 only
- D. Category4 and Category5 only
Answer: B
NEW QUESTION # 145
You have a Microsoft 365 E5 tenant that contains the policies shown in the following table.
A file named File1 has all the policies applied.
How long will File1 be retained?
- A. File1 will be deleted automatically after seven years.
- B. File1 will be retained until the file is deleted manually.
- C. File1 will be deleted automatically after five years.
- D. File1 will be deleted automatically after 10 years.
Answer: D
NEW QUESTION # 146
You have a Microsoft 365 subscription.
You identify the following data loss prevention (DLP) requirements:
* Send notifications to users if they attempt to send attachments that contain an EU Social Security Number (SSN) or Equivalent ID.
* Prevent any email messages that contain credit card numbers from being sent outside your organization.
* Block the external sharing of Microsoft OneDrive content that contains EU passport numbers.
* Send administrators email alerts if any rule matches occur.
What is the minimum number of DLP policies and rules you must create to meet the requirements? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: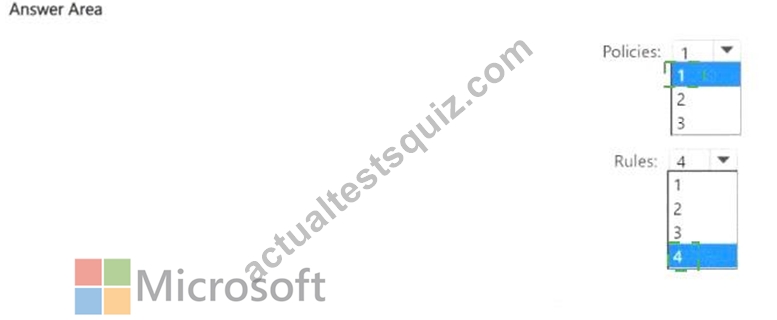
NEW QUESTION # 147
You create a sensitivity label as shown in the Sensitivity Label exhibit.
You create an auto-labeling policy as shown in the Auto Labeling Policy exhibit.
A user sends the following email:
From: [email protected]
To: [email protected]
Subject: Address List
Message Body:
Here are the lists that you requested.
Attachments:
<<File1.docx>>
<<File2.xml>>
Both attachments contain lists of IP addresses.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: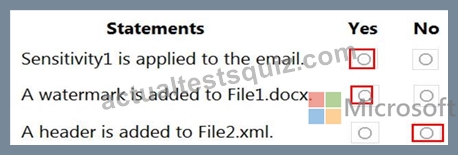
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365-worldwide
NEW QUESTION # 148
......
Get Top-Rated Microsoft SC-400 Exam Dumps Now: https://www.actualtestsquiz.com/SC-400-test-torrent.html
Pass Your SC-400 Dumps Free Latest Microsoft Practice Tests: https://drive.google.com/open?id=14IAKvJj01UqfVeCHo9pCAsvGkWXkPHp7
